Security teams use many tools, but they often lack a shared, comprehensive view of credential risk.
After all, identity providers (IdPs) and endpoint detection and response (EDR) tools weren't built to see what happens inside the browser, where employees spend the majority of their work day. These tools can tell you if a login succeeded or a device is compromised, but they can't tell you if a credential was weak, reused, or entered on a phishing site.
That gap leaves a blind spot in the SIEM, regardless of which platform a security team uses.
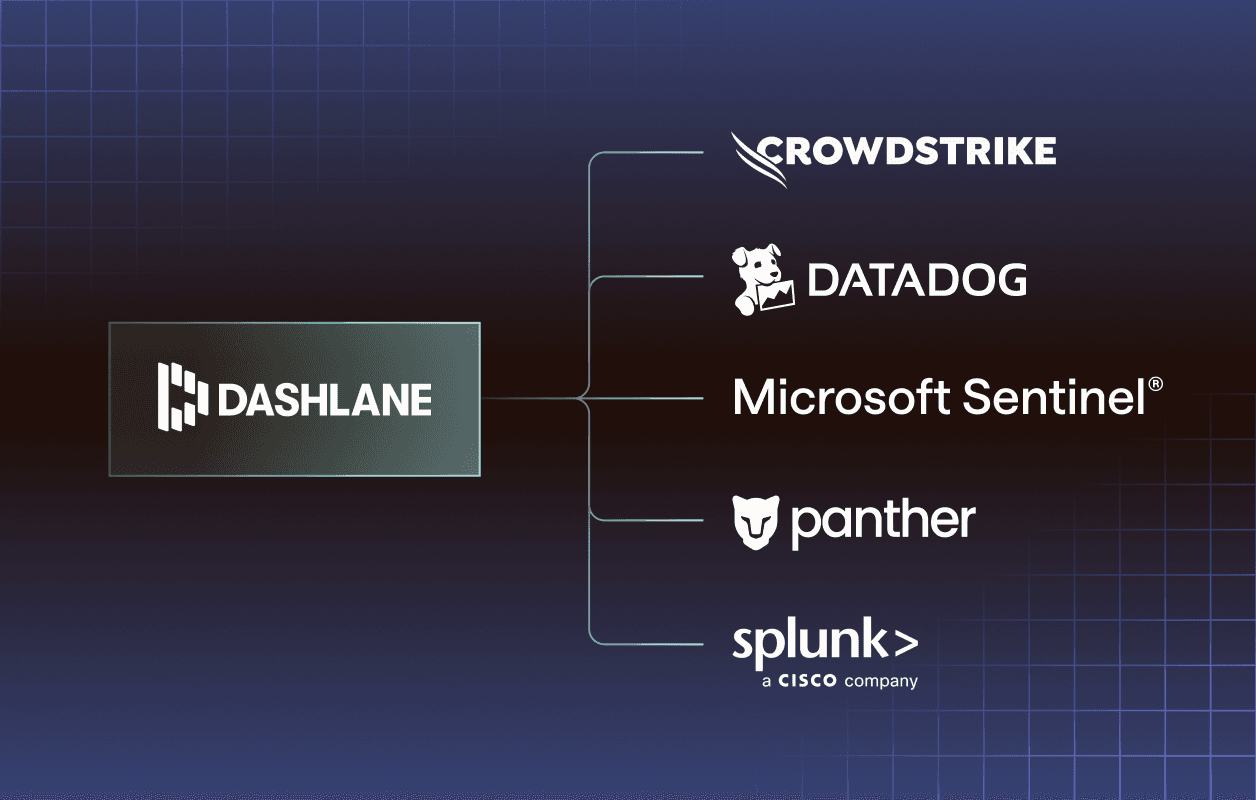
Dashlane has closed that gap. Panther SIEM, DataDog Cloud SIEM, and Crowdstrike Falcon® Next-Gen SIEM join Microsoft Sentinel and Splunk on Dashlane Omnix®’s growing list of integrations. Get credential risk telemetry directly in the SIEM tool your security team already leverages, making credential risk a native signal across your security stack.
The blind spot, explained
Three problems show up again and again for security teams:
- Browser-based credential risk is invisible to the SIEM. IdPs and EDR tools can’t see credential risk telemetry generated in the browser, so that signal never reaches the SIEM in the first place.
- Shadow IT and unmanaged SaaS logins go untracked. Without a credential telemetry source for apps outside the sanctioned stack, those logins never appear in the SIEM at all.
- Credential data lives in a silo, regardless of the SOC tool. Investigating a credential-related incident requires pulling context from a separate password management console, correlating events by hand, and rebuilding timelines manually. This adds complexity and workload when speed matters most.
Five SIEM integrations, one consistent workflow
Once Omnix is integrated with Microsoft Sentinel, Splunk, Panther, Datadog, or CrowdStrike, credential risk stops being a blind spot. Here's how.
- Browser-native telemetry, portable across the stack: Omnix captures credential events—from at-risk credential usage and visits to suspected phishing domains—in the moment, regardless of SSO or vault use. And those signals are portable across whichever SIEM your security team runs.
- Last-mile phishing protection, wherever analysts triage: Omnix's proprietary AI phishing model evaluates suspicious sites before credentials are entered and alerts employees, and those enriched events show up natively in your SIEM.
- Centralized risk visibility, regardless of stack: Credential events correlate with identity, endpoint, network, cloud, and observability data already flowing through your SIEM tool.
- Faster detection and remediation: The credential risks that used to take days or weeks to detect now take seconds, and automated triage and response are available wherever the team already works.
- No new tools: There’s no new console to learn or manage. Everything stays consistent.
The bigger picture
Browser-native credential telemetry is becoming a standard signal in the modern SOC, the same way EDR or identity logs already are.
Whichever tool your security team already relies on, credential risk no longer has to be the blind spot.
Sign up to receive news and updates about Dashlane